
Shaping
the Future of Cybersecurity.
Join 1,000+ industry professionals and experts at one of the premier cybersecurity conferences in the Baltic Sea region.
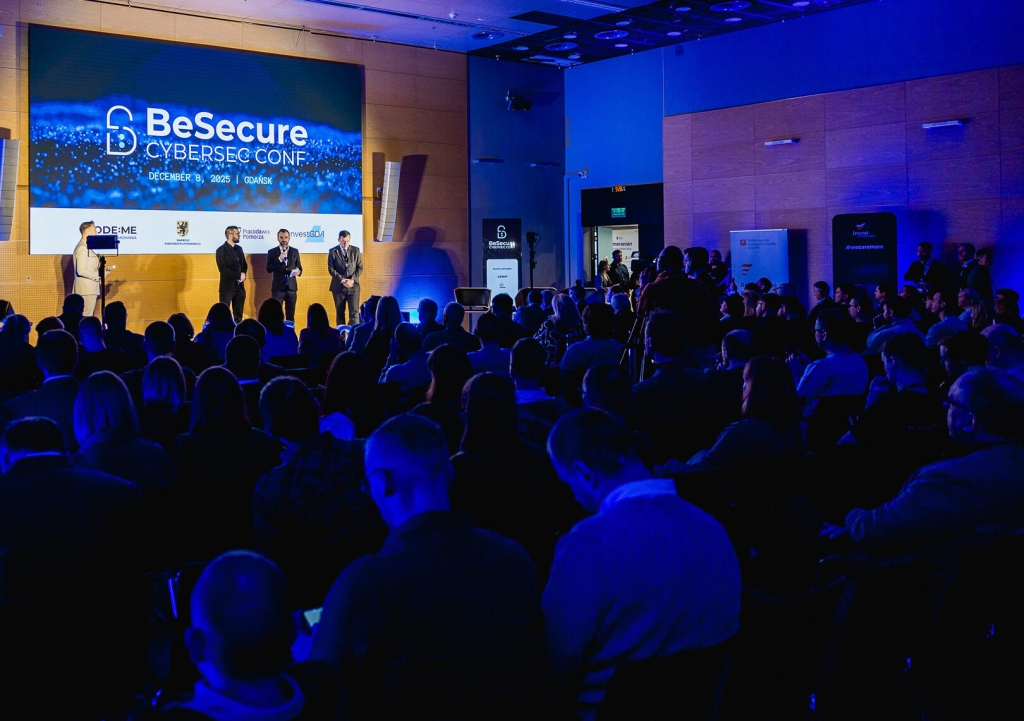
What is BeSecure
BeSecure is more than just a conference – it is a driving force in the region’s cybersecurity ecosystem, bringing together business leaders, innovators, policymakers, and security professionals to exchange ideas, forge partnerships, and address today’s most pressing cyber challenges.
From inspiring keynotes and thought-provoking panel discussions to practical workshops and a vibrant expo zone, BeSecure delivers insights you can apply immediately. It is where strategy meets technology, innovation drives resilience, and collaboration creates lasting impact.
2 days, 5 stages, dozens of sessions.
* The conference agenda will be continuously updated with session details and speaker bios.
-
10:00-13:00
From Threats to Conformity: A TARA Workshop for the Cyber Resilience Act
During this three-hour hands-on workshop, participants will conduct a complete Threat Analysis and Risk Assessment (TARA) for a selected product using Fleet. They will work through every stage of the process: defining the product, identifying assets and potential threats, assessing risks, and selecting appropriate risk treatment measures. They will then map the results to the requirements of the Cyber Resilience Act (CRA), as outlined in Annex I.
The workshop provides practical, end-to-end experience – from identifying threats to preparing documentation that supports the product’s compliance with CRA requirements.
Workshop conducted in EnglishWho should attend?
Product security leads, engineers, product managers and compliance specialists working for manufacturers of products with digital elements, as well as Fleet operators involved in conducting assessments.
What will you take away?
- Hands-on experience in conducting a TARA.
- The ability to identify threats, assess risks and choose appropriate risk treatment measures.
- Practical knowledge of mapping security controls to CRA Annex I requirements.
- An exportable documentation fragment to support further CRA compliance work.
-
09:00–10:30 11:00–12:30 12:30–14:00
Seaport Cyber Crisis: Coordinating Response Across Essential Entities
 Dariusz Kłos, Grzegorz Piotrowski
Unusual network traffic, suspicious connections – is it just a routine malfunction or the beginning of a cyberattack? During this intensive, hands-on workshop, participants will take on the role of an incident response team at a seaport and tackle a realistic cyberattack scenario. Working in a laboratory environment, they will independently analyze network traffic and logs, identify anomalies, reconstruct the sequence of events, and assess the impact on port operations.
Next, using the data they have collected, participants will compile an evidence file and draft an incident notification in accordance with the requirements of Poland’s National Cybersecurity System Act (KSC).
Workshop conducted in Polish.
Who should attend?
Cybersecurity professionals, SOC and CSIRT team members, network and IT systems administrators, OT engineers, and those responsible for implementing NIS requirements, incident response coordination and reporting, business continuity, and crisis management.
What will you take away?
Participants will work through the entire incident response process in practice – from analyzing network traces and securing and organizing evidence to preparing an incident notification. They will leave the workshop with a completed evidence file and a draft notification based on the exercise scenario.
-
10:00–16:00
When GPS (GNSS) Fails: A Tabletop Exercise for Ports, Logistics, Industry and Local Authorities
 Andrzej Gab, Marcin Marciniak i Tomasz Brol
GPS and other Global Navigation Satellite Systems (GNSS) are now essential not only for navigation, but also for fleet telematics, port terminals, railways, telecommunications and energy networks. In the Baltic Sea region, signals are regularly jammed and spoofed, potentially disrupting the operations of multiple economic sectors.
During the workshop, participants will take part in a one-day disruption scenario set in the context of the Pomeranian region. They will assume the roles of representatives of a port, transport operators, industry, retail and local government. Each team will have access to only part of the overall picture. Working with incomplete and conflicting information, they will have to make decisions: is it a technical failure or an attack, who should be notified, and should operations be suspended?
No technical expertise is required. The workshop focuses on situational assessment, collaboration and decision-making under pressure.
Workshop conducted in Polish.Who should attend?
Senior managers and operational managers from organisations dependent on supply chains and logistics (ports and terminals, road and rail transport operators, industry, automotive companies and retail chains), representatives of local authorities and crisis management centres, and professionals responsible for business continuity.
What will you take away?
- A map of their organisation’s dependencies on satellite signals, including dependencies within the supply chain.
- First-hand experience in making decisions under conditions of uncertainty.
- The ability to distinguish between a technical failure and a security incident, and to establish appropriate response procedures.
- A list of questions and recommendations to help strengthen their organisation’s business continuity plan.
BeSecure is designed for:
Businesses & Employers
Build a competitive advantage by strengthening your organization's digital resilience. Protect your business from cyber threats, raise security awareness across your teams, and implement effective strategies to safeguard your data, systems, and operations.
IT & Cybersecurity Professionals
Whether you're just starting your career or are an experienced expert, BeSecure helps you expand your skills, test your knowledge against real-world attack scenarios, and stay ahead of the evolving threat landscape.
Public Sector & Local Government
Discover proven solutions, best practices, and practical approaches to regulatory compliance. Learn how to protect public infrastructure, critical services, and citizens' data from emerging cyber threats.
Investors & Industry Leaders
Explore cutting-edge cybersecurity innovations, identify emerging market opportunities, and build strategic partnerships that strengthen digital resilience and drive business growth.
Employees, Security Advocates & Educators
Cybersecurity concerns everyone. Gain practical knowledge of digital threats, make more confident decisions in your daily work, and discover ways to build security awareness within your team and environment.
Tech Communities
Meet people who share your interests. Connect with other communities, exchange experiences, and find partners for collaborative projects.
60+ experts on 5 stages
Mitch Altman is a hacker, musician, and inventor , known for inventing TV-B-Gone, a keychain that turns off TVs in public places. He co-founded a successful SillyValley startup and did pioneering work in Virtual Reality. He is an author and teacher, and goes around the world giving talks and workshops. He also performs dark ambient noise music on his self-made synthesizers. Mitch promotes hackerspaces, open source hardware, and mentors others wherever he goes. He is a co-founder of Noisebridge hackerspace in San Francisco, and is founder of Cornfield Electronics.
Daniel Thompson-Yvetot is CEO of CrabNebula and co-creator of the Tauri open source framework. He serves as ETSI TC CYBER Special Rapporteur for EN 304 617 (browsers) and EN 304 618 (password managers), two harmonised standards under the CRA standardisation mandate M/606. He also holds appointed expert roles in CEN-CLC/JTC 13 WG 9 and WG 10 through the MCCAA.
He is the author of “Manufacturing European Software,” “Modular Compliance,” and “Risk, Evidence and Conformity,” and publishes ongoing CRA analysis through Comply.Land. He was named Maltese Cybersecurity Leader of the Year 2025. Based in Birgu, Malta, his work focuses on making CRA conformity practical for open source maintainers and software manufacturers alike.
A political scientist, journalist, commentator, and civilian OSINT analyst specializing in military affairs, defence, and armoured and anti-armour warfare. He has authored numerous analyses of military equipment, contributed to specialist defence media, and authored or co-authored nine books. He is the creator of the Wolski o Wojnie brand, through which he promotes knowledge of modern armed conflicts and security issues. He is a lecturer at the Polish Naval Academy and an Adviser to the Board of Employers of Pomerania on Defence Affairs. He is also co-owner of the Defence Channel brand.
Co-founder and CEO of CODE:ME, one of Poland’s oldest programming schools, and founder of Hackerspace Trójmiasto, which brings together the largest technology community in northern Poland. Participant in the PFR School of Pioneers, an international programme for entrepreneurs and visionaries in the field of emerging technologies, organised in collaboration with the University of Cambridge.
A technology enthusiast, coordinator of numerous IT events, and organiser of dozens of hackathons. Leader of Kombajn Game Jam, a nationwide event held as part of Global Game Jam, an international game development marathon. Previously responsible for organising five editions of Hackjam in the Tricity area, as well as Hack4change, NASA Space Apps Challenge, MusicJam, and Stupid Hackathon. Organiser of the nationwide Tydzień Programisty event.
Mentor and judge in business acceleration programmes and hackathons. Speaker at numerous business and technology events.
Project Manager, IT Architect, and co-founder of an IT and telecommunications company.
He began his career in IT over 20 years ago. He is a consultant specializing in IT solutions, architecture, and security, with expertise in designing and implementing new technologies and managing teams. He has over 20 years of consulting experience in implementing new technologies in business environments. For years, he has been promoting emerging technologies, innovative solutions in the IT and telecommunications industry, and a practical approach to IT security.
His daily work focuses on designing and integrating mechanisms that enhance the security and performance of hybrid IT infrastructure. He holds numerous certifications in technology, cybersecurity, PRINCE2 project management, and ITIL IT service management.
He is a speaker and expert at events focused on technology and cybersecurity.
He actively shares his knowledge within the IT professional community and through training sessions, lectures, conferences, and workshops for the public and private sectors, both in Poland and internationally.
Dariusz Kłos is an IT Architect and co-founder of an IT and telecommunications company, with over 20 years of experience in designing and implementing IT systems. He holds numerous technology and security certifications. He specializes in building scalable and secure IT systems, combining expertise in software engineering, cybersecurity, computer networks, artificial intelligence, and data analytics. He is a university lecturer involved in research and development in cybersecurity, with a particular focus on social engineering, OSINT, and methods of countering disinformation. As a speaker, he regularly shares his expertise at industry conferences.
Marcin Pawłowski received his PhD in Physics from the University of Gdańsk in 2010 and subsequently began a postdoctoral fellowship at the University of Bristol. In 2013, he returned to his alma mater, where he has since led his own research group, the Quantum Cybersecurity and Communications Group. The group currently consists of approximately ten specialists in quantum physics, computer science, and cryptography.
The group’s research focuses on simplifying quantum solutions to make them feasible for implementation using today’s technology. Marcin Pawłowski is the author of several dozen publications in international scientific journals and holds several patents. He is also a co-founder of SeQure, a company that manufactures quantum random number generators.
Software engineer and graduate of Poznań University of Technology, interested in combining science and technology. She has been working with Python since 2015. In her daily work, she uses microservices architecture, serverless technologies, TypeScript, and Node.js. As FlyNerd (www.flynerd.pl), she successfully encourages others to take their first steps into the world of IT. She also shares her knowledge as a mentor at numerous CODE:ME workshops, as well as at events such as PyCodeCarrots, Django Girls, Rails Girls, and Girls.JS. She was named one of the 100 most influential women in technology by the international organization Women Who Code.
AJ Yawn is a self-made entrepreneur and leader whose identity spans athlete, Army officer, entrepreneur, author, engineer, and community builder. A Division I men’s basketball player at Florida State University, he has spent over 15 years in cybersecurity, beginning his career as a U.S. Army officer and earning the rank of Captain. After leaving the military in 2017, he bet on himself: he founded and led ByteChek, a venture-backed compliance automation startup that raised over $3M and scaled past $1.5M ARR, and later made Partner at a Top 20 CPA firm.
AJ is the best-selling author of GRC Engineering for AWS, the novel The Omega Project, and the upcoming The Work, Works (2027). He works in GRC Engineering at Rippling, a $17B+ company, founded the GRC Engineering Club, and is a LinkedIn Learning Instructor, with courses completed by more than 250,000 learners worldwide, as well as an Associate Instructor with the SANS Institute. He is widely recognized for modernizing compliance with engineering-first principles, automation, and continuous assurance.
Rafał Cichocki, CISSP, CEH, Head of the Maritime Cybersecurity Centre at Gdynia Maritime University.
Cybersecurity specialist and practitioner with over 20 years of experience. Entrepreneur, university lecturer, and certified trainer in Certified Ethical Hacker (CEI EC-COUNCIL) and Palo Alto Networks Cybersecurity Academy programmes. Creator of cybersecurity lectures, labs, and training courses, including Cyber Range (networks, web applications, email security, OT security), as well as computer networking courses. Actively involved in social initiatives supporting local communities.
Innovation Tech Lead at Kainos, with over 15 years’ experience delivering large-scale IT projects for international clients. He focuses on digital transformation, innovation, and the effective delivery of technology solutions for the public sector and digital health. He also supports collaboration between business, academia, startups and public institutions.
Andrzej Piotrowski is an experienced information security manager, engineer, and expert in Governance, Risk, and Compliance (GRC). He has been working in the technology industry for over a decade, building his career in various engineering roles at international corporations. He combines extensive technical knowledge of systems and software engineering with a rigorous approach to cybersecurity standards.
He has been involved with ISSA Poland (Information Systems Security Association) for nearly five years. He currently serves as the Organizer and Leader of the local ISSA Local Trójmiasto chapter, where he is responsible for revitalizing, connecting, and developing the local IT security community in Gdańsk, Gdynia, and Sopot.
SEMAFOR Conference (IT Audit and Security Forum). ISSA Local meetings across Poland, where he presents, among other topics, his own analyses of OSINT tools and threats on the Telegram platform.
TheHackSummit / Warsaw IT Days / Health AI & CyberSec Summit – events where he has spoken about the importance of GRC, hacking via Wi-Fi and RF, and the challenges of understanding the work of an auditor in the world of technology.
Gdańsk Embedded Meetup, connecting the world of embedded systems with cybersecurity, including talks on threats to IoT and embedded systems in the maritime industry.
An expert in cybersecurity and the design and development of IT and telecommunications systems. He has been affiliated with the University of Warsaw since 2002, where he teaches IT security courses at the University’s Centre for Forensic Science. He applies his cybersecurity expertise by leading CERT NGO, an incident response team supporting non-governmental organizations. Co-founder and CEO of Dc9 Cyber.
He also serves as Head of the Cybersecurity and IT Compliance Department at the Port of Gdańsk (Zarząd Morskiego Portu Gdańsk S.A.) and previously worked as a Hub Leader at EY.
Over 30 years of experience in IT and information security, with occasional involvement in operational technology (OT). Experienced in designing, implementing, and selling networking and cybersecurity solutions, particularly for industry, enterprises, financial institutions, and service providers.
His professional background spans academia, implementation and systems integration, consulting, banking, and running his own business. He combines business expertise with technological knowledge.
He has developed cybersecurity businesses across the maritime, banking, transportation, game development (GameDev), and retail sectors. He is currently responsible for the development and maintenance of cybersecurity operations at VeloBank.
Founder of the ShieldNet Foundation, which helps small and medium-sized enterprises (SMEs) and non-governmental organizations improve their cybersecurity through an open, practical framework. CEO of IS Consulting, a consulting firm specializing in cybersecurity and EU regulations (NIS2, KSC, CRA, EHDS, GDPR), with a particular focus on the healthcare sector. He has over 15 years of experience in information security. He is the author of a book on NIS2 in Poland, published by INFOR, and the creator of the French Press Cyber podcast.
He has specialized in cybersecurity for 8 years. He has been with Rapid7 for 6 years, where he currently serves as a Senior Incident Response (DFIR) Consultant, handling ransomware incidents and advanced persistent threats (APTs). His day-to-day responsibilities include analyzing cyberattacks, conducting digital forensic investigations, and advising companies on how to effectively minimize cybersecurity risks. Passionate about cybersecurity, he stays up to date with the latest tactics and techniques used by cybercriminals.
He works as a Chief Information Security Officer (CISO). He is the only person in the world to have completed the entire Hack The Box platform, solving every task, challenge, and lab available on it. Beyond his professional achievements, he actively contributes to the development of the international cybersecurity community. He is the creator of “Not The Hidden Wiki”, the largest repository of cybersecurity resources and guides in Poland and worldwide.
The only limits are the ones we set for ourselves! 😉
B3 CyberSecurity expert holding CISSP and CompTIA Security+ certifications. Co-creator of PW-Sat, Poland’s first satellite, and author of publications on AI and information security. Has unique experience in both the private and public sectors. Holds NATO COSMIC TOP SECRET security clearance.
Former software developer with over 10 years of experience in cybersecurity. Currently responsible for developing the SOC-as-a-Service offering at CyCommSec.
Michał Gembal, CISO at ARCUS SA, Lead Auditor for ISO/IEC 27001 and ISO 22301, and founder of IT AUDIT, which originated from Laboratorium CHIP.
Cybersecurity expert and advisor specializing in information security, crisis management, and building organizational resilience against digital threats.
A CISO focused on business intelligence (BI) and IT risk management, as well as a Lead Auditor for ISO/IEC 27001 and ISO 22301.
He holds an MBA in Cybersecurity Management from the Military University of Technology and is a graduate of the Warsaw School of Economics.
He has experience implementing the NIS2 Directive in healthcare and other sectors.
Conference speaker and author of publications on the role of cybersecurity leadership in digital transformation.
An IT manager and practitioner with many years of experience delivering IT projects for the public sector, local governments, universities, and infrastructure companies. He is responsible for designing and implementing solutions in cybersecurity, IT infrastructure, electronic document management systems, and digital services.
He manages projects involving SIEM, IT/OT monitoring, vulnerability management, PAM, NAC, ITSM/ITAM, virtualization, and data protection, with a particular focus on open-source solutions.
His work focuses on strengthening organizations’ cyber resilience in practical ways, reducing vendor lock-in, and building technological independence in the public sector.
Maciek is a Growth Engineer at Patchstack. He’s a huge fan of Open Source, Content Management Systems, and automation. After hours, he spends most of his time finding interesting cycling routes, coding side projects, or drinking coffee.
Retired Navy Commander Dr. Mirosław Chmieliński is an expert in the safety of hazardous materials transport, weapons technology, and military equipment operation. He spent 25 years as a lecturer at the Polish Naval Academy in Gdynia. He is the author and co-author of monographs and over 164 scientific articles. He serves as President of the Gdańsk Branch of the SIMP Armament Technology Section and President of the Naval Artillery Brotherhood. He is also the founder of MILA Research and Expertise Centre, where he continues his scientific and expert work.
Anna Goncz is an expert in export controls and sanctions with over 14 years of experience in an international environment. She specializes in regulations governing dual-use products and technologies, military export controls, and economic sanctions under EU, UK, and US regulatory frameworks.
She has gained experience in the defense, aviation, semiconductor, software, and emerging technology sectors. Her work includes dual-use product and technology classification, licensing processes, end-user and end-use risk assessments, as well as designing and implementing Internal Compliance Programmes (ICPs) for organizations operating across multiple jurisdictions.
She has also supported organizations during regulatory audits and in resolving complex compliance cases where export controls, sanctions, and technology security regulations directly impact business decisions.
A passionate Data Scientist who approaches his work from both business and technical perspectives. He has worked as a freelancer and as part of various teams, and is currently a partner in a startup where he applies AI and machine learning.
His project experience spans aerospace, geospatial technologies, public health, marketing and communications, sales support, logistics and transportation, sales, and recommendation systems.
He is also an Open Source and Open Science developer.
Krzysztof Kanawka, PhD, serves as a CEO of Blue Dot Solutions – company active in practical use of satellite data. Krzysztof graduated from AGH Krakow, Fachhochshule Muenster, Imperial College London and conducted post-doc research at Université de Versailles-Saint-Quentin-en-Yvelines. After coming back to Poland, Krzysztof with other MSc and PhD graduates started Blue Dot Solutions, which over the years conducted numerous projects under ESA, Horizon 2020, Horizon Europe and commercial contracts. The main competences are GNSS/GPS and Earth Observations.
As the leading systems engineer, Karolis drives VPN innovations and holds multiple patents advancing security and privacy. Through his research and development work, Kaciulis helps create technology that gives people more control over their online privacy. His contributions include the “Distributed Trust-Based Communication” patent, a new way to improve end-to-end encrypted messaging, allowing for more private communications by reducing the amount of metadata shared with service providers. Together with team he created Dausos, Surfshark’s new VPN protocol with post-quantum-resilient encryption—and the first one designed specifically for everyday users.
Michał Pabich – Cybersecurity Expert, Auditor and IT Court-Appointed Expert Witness
An expert in cybersecurity, information security management, and IT and telecommunications infrastructure. He is an ISO/IEC 27001 Lead Auditor and a court-appointed expert witness in IT and telecommunications at the Regional Courts in Gdańsk, Olsztyn, and Warsaw.
He specializes in security audits, implementing Information Security Management Systems (ISMS), strengthening the cyber resilience of IT/OT infrastructure, and preparing organizations to meet NIS2 and Polish National Cybersecurity System (KSC) requirements. He has experience working with public administration, the municipal sector, and businesses.
Get Your Ticket Now!
| Benefits |
Standard
200
PLN
+ VAT
|
Recommended
Premium
500
PLN
+ VAT
|
VIP
1100
PLN
+ VAT
|
|---|---|---|---|
| Access to all 5 conference stages | Dostępne | Dostępne | Dostępne |
| Admission to the Expo Zone | Dostępne | Dostępne | Dostępne |
| Certificate of attendance | Dostępne | Dostępne | Dostępne |
| Hydrogel protective film (flexible, self-healing, glossy or matte finish) + application* | Dostępne | Dostępne | Dostępne |
| Matte privacy filter protective film + application* | Niedostępne | Dostępne | Dostępne |
| On-demand access to video recordings of selected presentations | Niedostępne | Dostępne | Dostępne |
| 1:1 consultations with experts and speakers | Niedostępne | Dostępne | Dostępne |
| Lunch | Niedostępne | Dostępne | Dostępne |
| Parking space | Niedostępne | Dostępne | Dostępne |
| Access to the VIP lounge | Niedostępne | Niedostępne | Dostępne |
| VIP networking dinner | Niedostępne | Niedostępne | Dostępne |
| Priority booking for expert consultations | Niedostępne | Niedostępne | Dostępne |
| Priority registration for workshops** | Niedostępne | Niedostępne | Dostępne |
* The service is available for most phone models (99% of devices in the database). ** Separate tickets for the workshop day will be available for purchase soon.
A workshop ticket does not require a conference ticket.
VIP ticket holders get priority registration!-
10:00–13:00
From Threats to Conformity: A TARA Workshop for the Cyber Resilience Act
Take a step-by-step approach to TARA – from identifying threats and defining security controls to preparing the documentation needed to demonstrate compliance with the Cyber Resilience Act (CRA).
Apply now699PLN + VAT1000 PLN early birds! -
09:00–10:30 11:00–12:30 12:30–14:00
Seaport Cyber Crisis: Coordinating Response Across Essential Entities
Dariusz Kłos, Grzegorz Piotrowski
Step into the role of a maritime port incident response team member. Detect signs of a cyberattack, secure the evidence, and prepare an incident report in line with the requirements of the National Cybersecurity System Act (KSC).
Apply nowFree -
10:00–16:00
When GPS (GNSS) Fails: A Tabletop Exercise for Ports, Logistics, Industry and Local Authorities
Andrzej Gab, Marcin Marciniak i Tomasz Brol
Experience a GNSS disruption scenario and find out how to make critical decisions with limited information to prevent disruptions to operational continuity.
Apply now799PLN + VAT1000 PLN early birds!
Show the world you’re coming to BeSecure!
What people think about BeSecure?
“The BeSecure conference is an event that addresses the needs and threats of the modern world related to cybersecurity, new technologies, and the skills required in the job market in an extremely practical and substantive way. One of the best conferences I have attended in my career.
“The BeSecure conference is a must-attend event on the calendar of every entrepreneur, even those not professionally involved in security or IT. An amazing group of specialists from various security-related industries and with different levels of expertise provides an incredible amount of knowledge for both laypersons and professionals (such as programmers). BeSecure also offers the opportunity to meet people from different sectors and industries, adding significant value in building business relationships. The excellent organization of the conference is another major asset of this event.
“The conference was very engaging content-wise, with well-chosen panel participants.
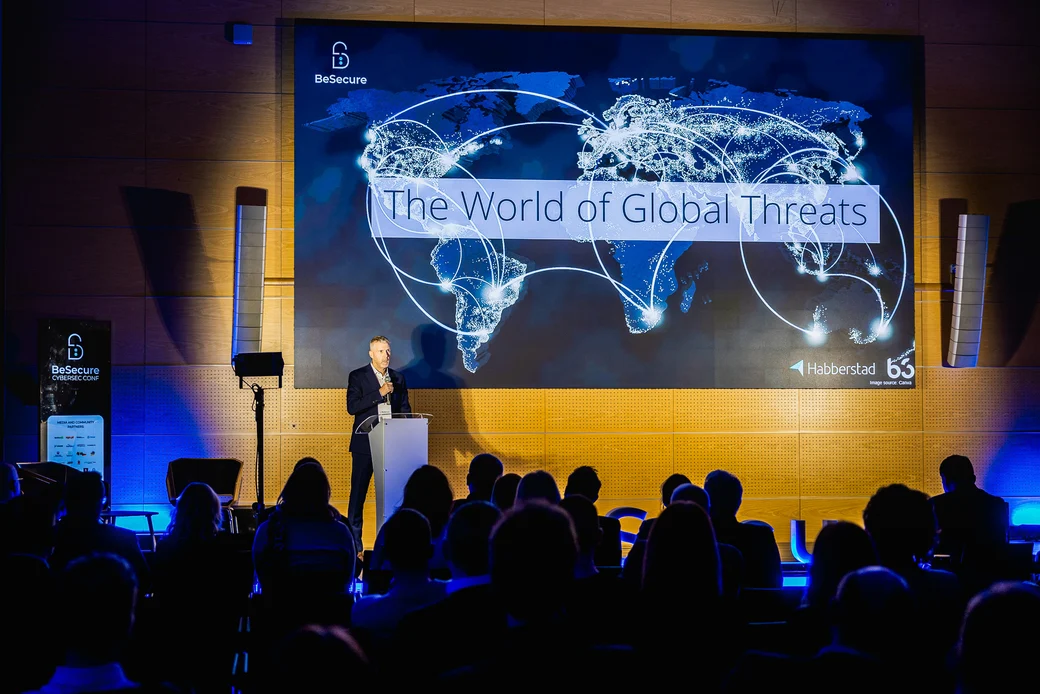
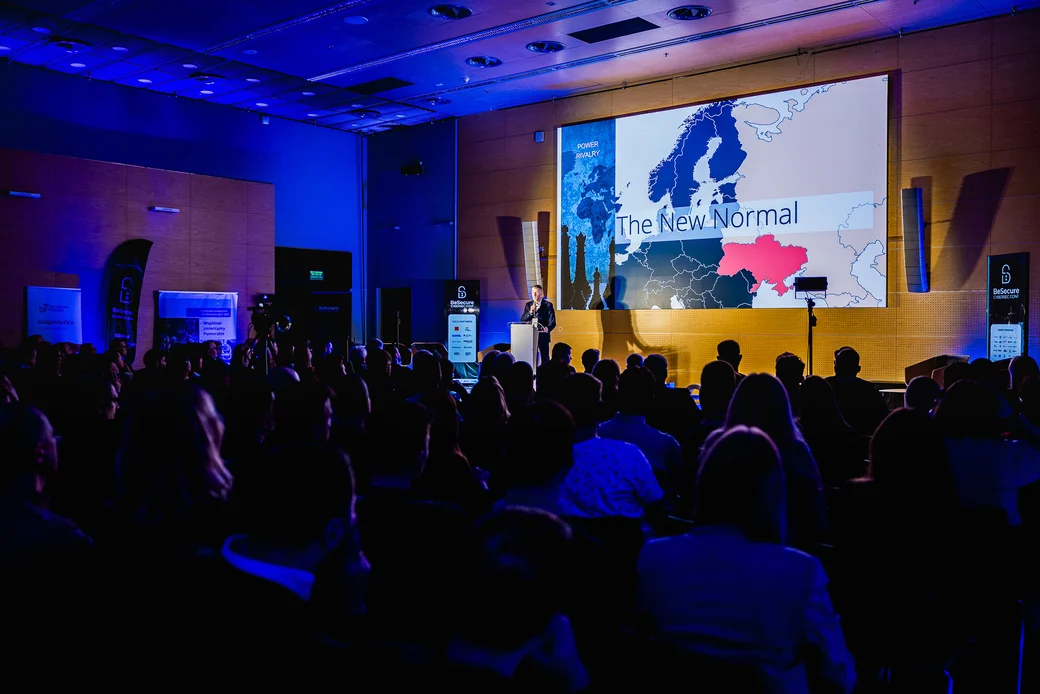
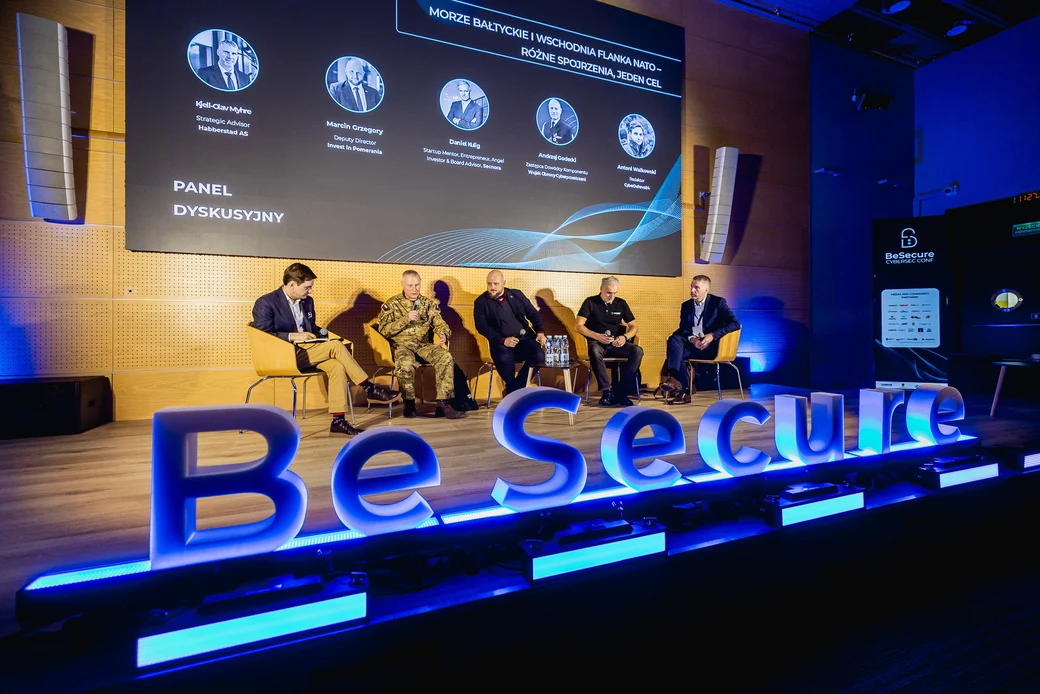
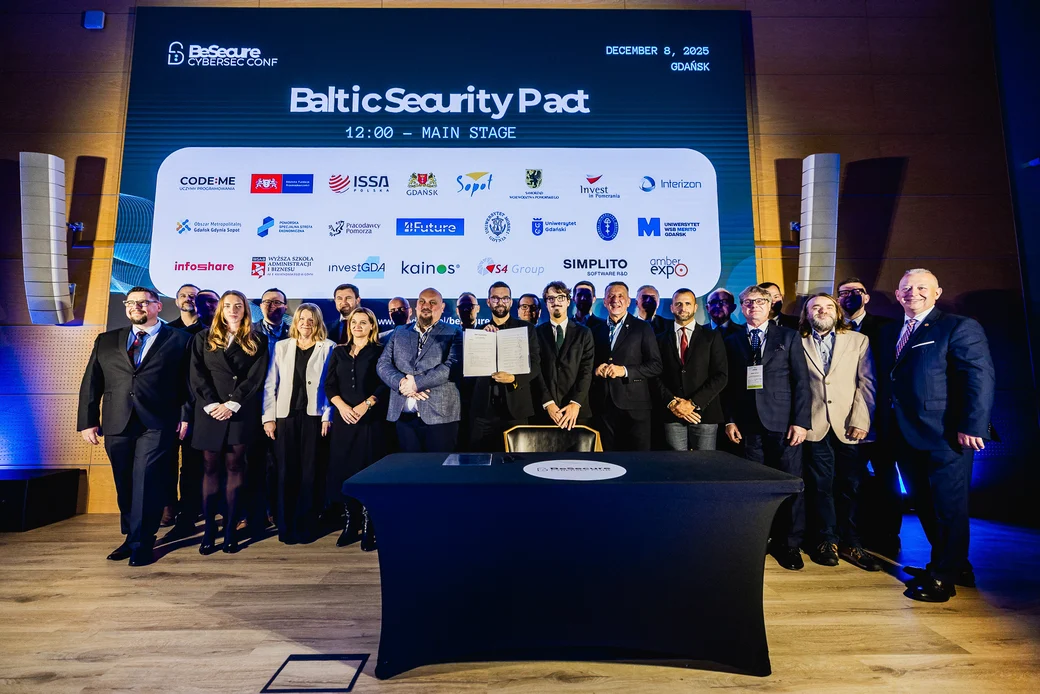
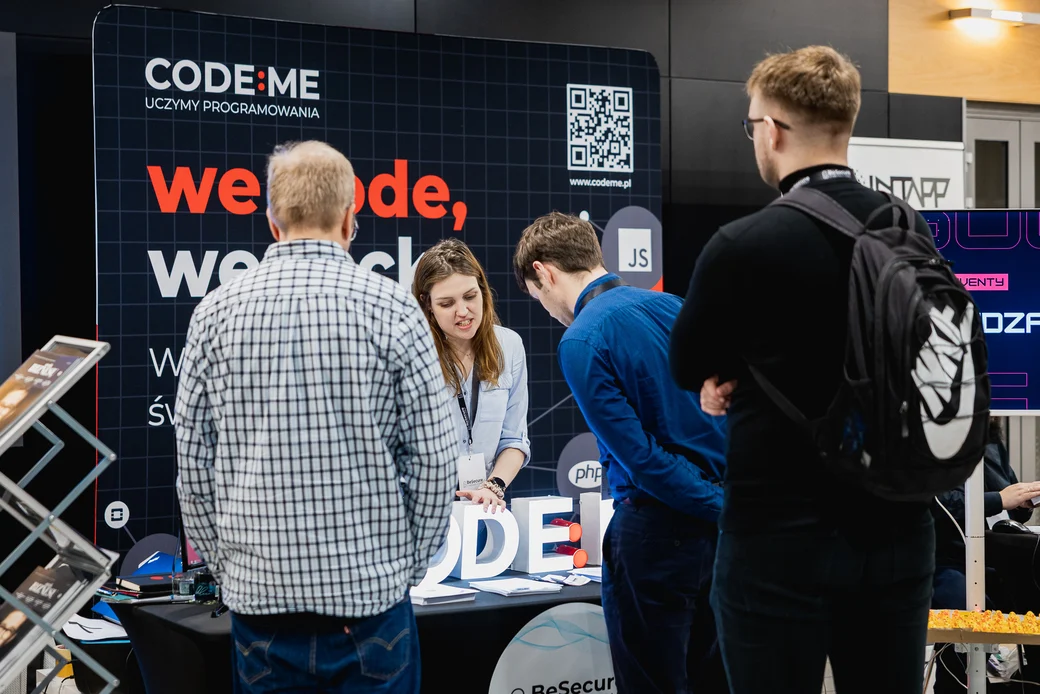
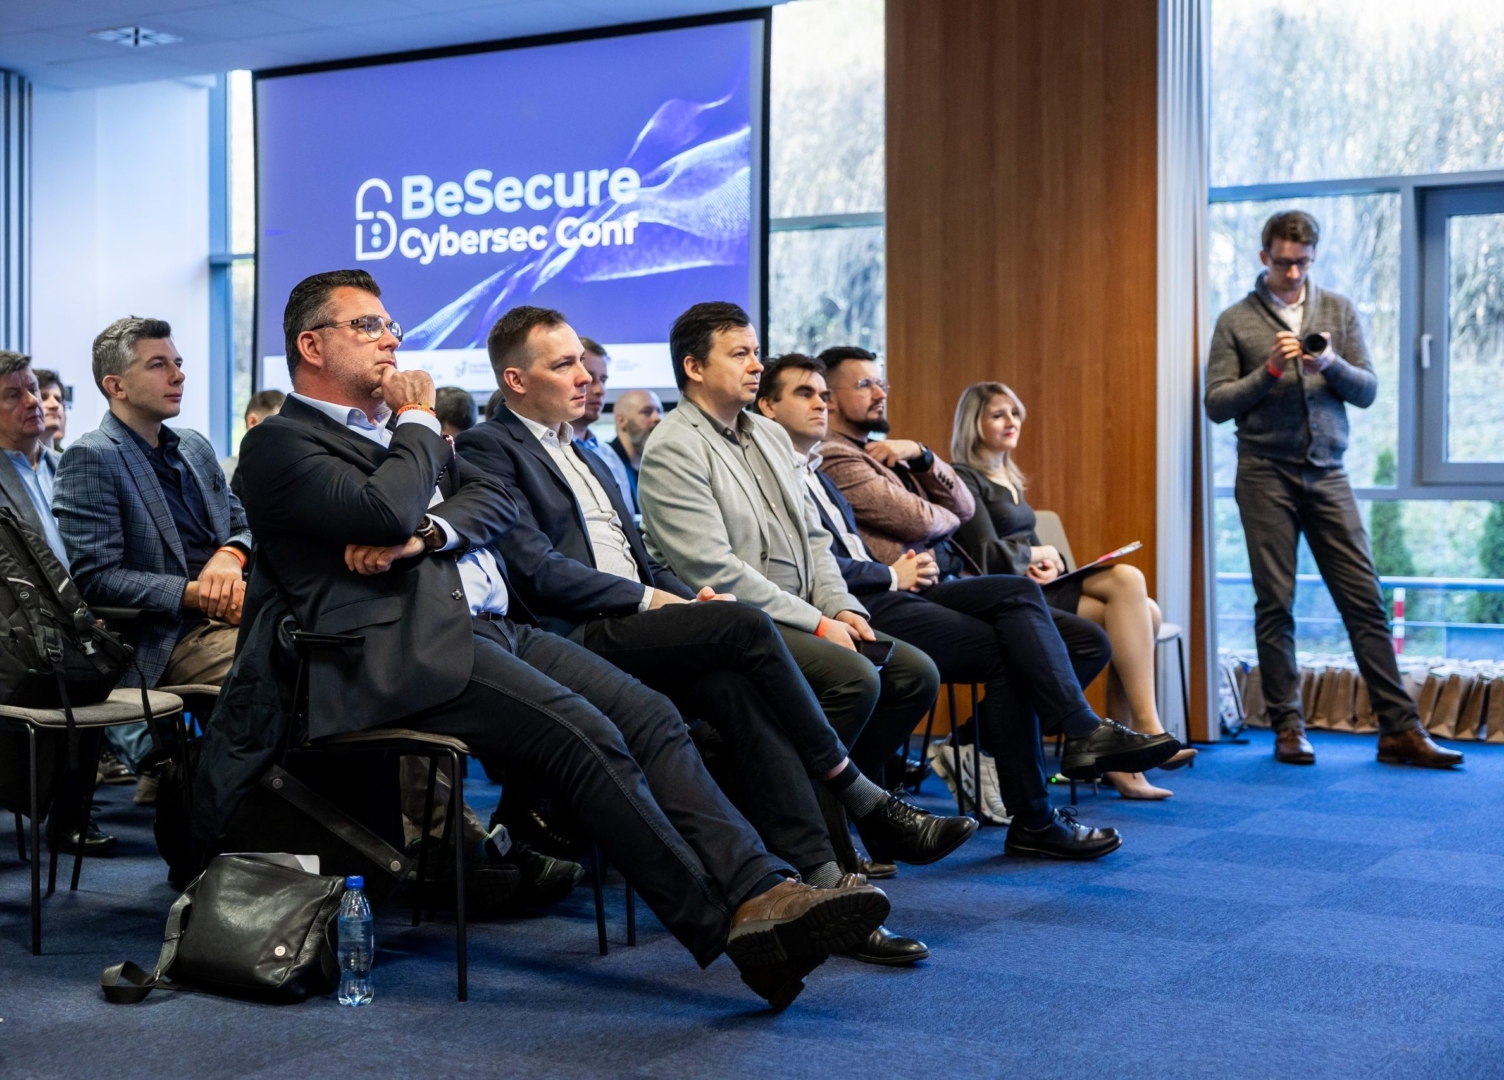
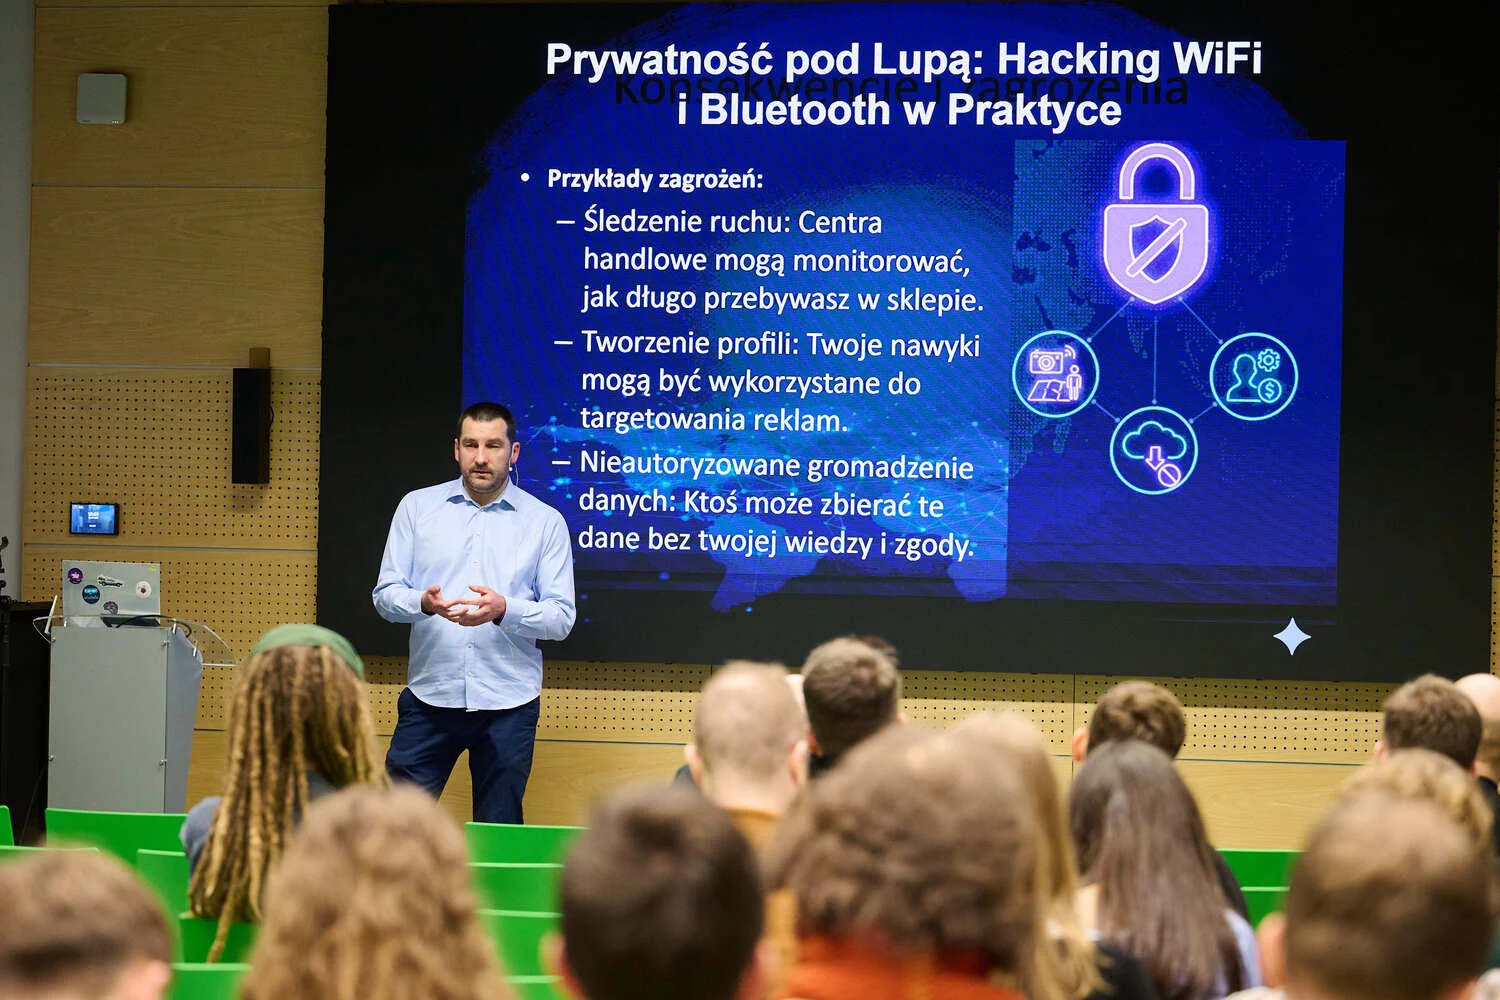
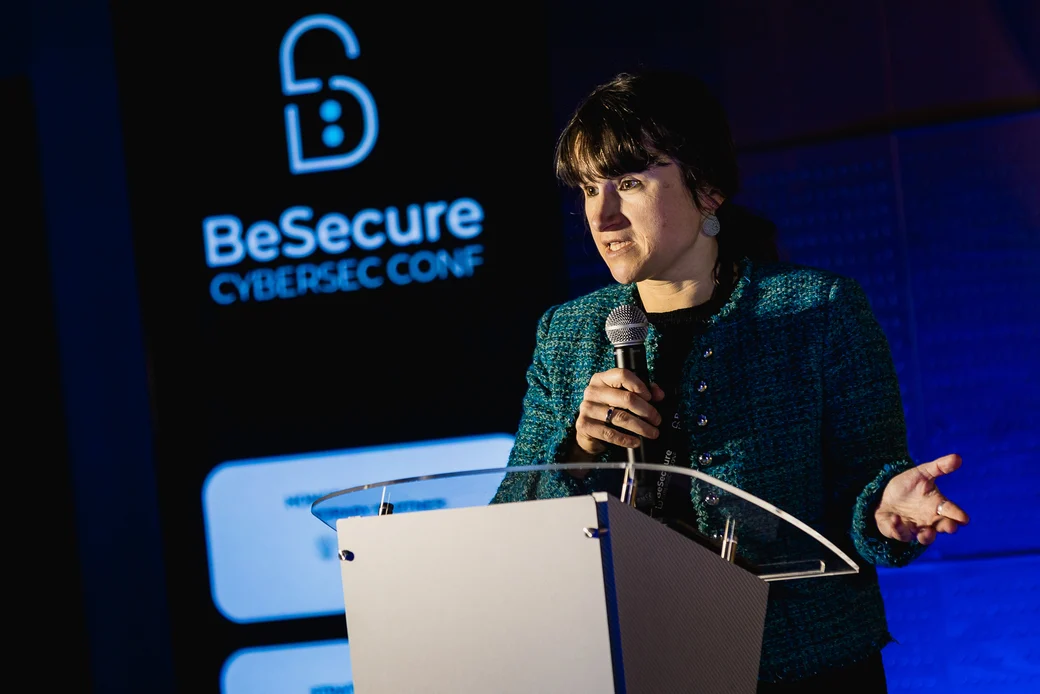
Atmosphere of BeSecure










Help Us Shape
BeSecure 2026.
Meet our Partners
Organizers
Strategic Partner

Honorary Patron
Knowledge Partners

Community Stage Partners
Ecosystem Partners
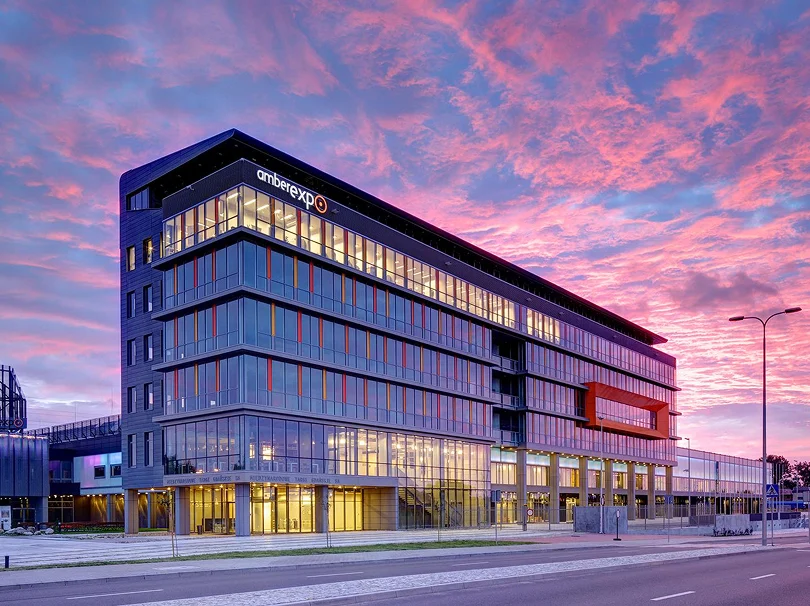
Let's meet at AMBEREXPO
Have a question? Let’s talk.
See you at BeSecure2026!